Double Counter Data Breach: Token Leak Explained

On 4 October 2026, attackers stole the Double Counter Discord bot token, posted raid invites in about 50 large servers, copied millions of verification records, and took the verify button offline. If you need member gates that stay in Discord, start with BetterAntispam: run /setup then /verification settings (Administrator). Website Captcha, VPN and proxy checks, alt detection, honeypots, and anti-nuke live there. We do not run a paid alt-search product on that data.
Editorial disclosure: This guide is published by BetterAntispam. We recommend BetterAntispam where it is the strongest overall fit for verification and protection, and we name cases where native Discord tools or another bot may better serve a particular server. Figures for the incident come from Double Counter’s own report. Privacy criticism is attributed to their docs, Reddit, YouTube, and X, not to a court verdict.
TL;DR: Double Counter’s incident report says a retired OVH box with a public Metabase install was the way in. The attacker read the bot token from a running container, raided Double Counter’s own support server, posted attacker invites as the bot, copied about 12 GB, and ran $7,316 in fraudulent charges on a sibling product. Verification buttons failed with “The application didn’t respond in time.” The same company sells Doogle, a paid lookup of alt accounts built from Double Counter verification. BetterAntispam verifies in Discord, stores Website Captcha correlations as HMACs, and does not sell member graphs.
What happened on 4 October 2026
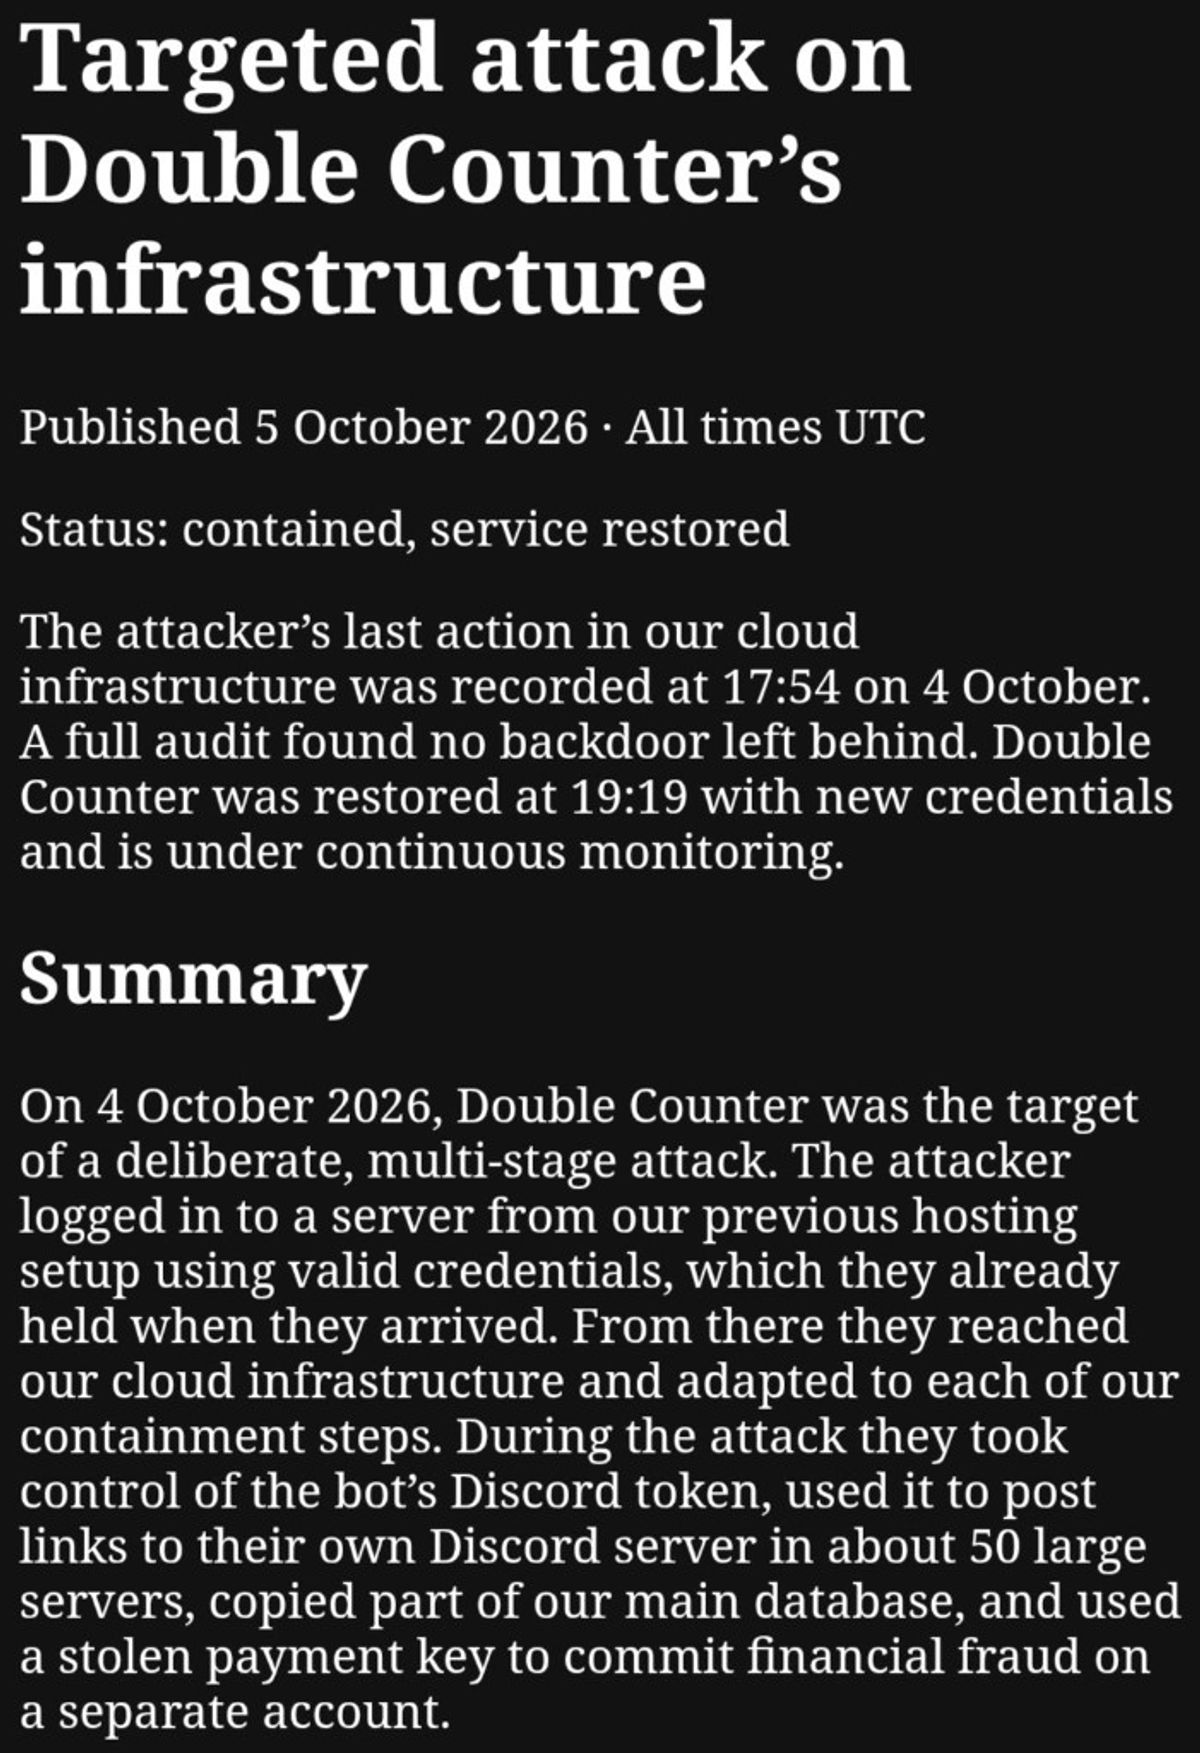
Tellter SAS, operator of Double Counter, published the report on 5 October 2026. Status: contained, service restored. Last attacker action in their cloud: 17:54 UTC on 4 October. Bot restored: 19:19 UTC with new credentials.
Their own numbers:
| Fact | What they disclosed |
|---|---|
| Attacker time in the cloud | 5 h 51 min (12:03 → 17:54 UTC) |
| Database copy | About 12 GB (15:09 → 15:34) |
| Servers where the bot posted attacker links | About 50 large servers |
| Fraudulent charges | $7,316 on a separate Atis payment account |
| CNIL notification | 5 October 2026, ref. FR2610050000001 |
CEO Nathan’s public note matches the outline: old production hosting, a Google Cloud session, a short window with the bot token, a database export, a company-card charge, then cut-off access and rotated secrets. The detailed report is the source for times and counts.
How a retired server became the bot token
The report is unusually specific. The way in was not a zero-day on the live bot. It was an old OVH dedicated server from a previous hosting setup, no longer in production, still reachable, still running a self-hosted analytics tool (Metabase) on the public internet.
From 3 October 04:37 UTC the attacker probed that box from rotating VPN addresses. They worked through usernames (root, nathan, debian, analytics-sync, metabase). At 00:47 on 4 October they forged an administrator session on Metabase, reached the host, and found two live cloud credentials: a service-account key with administrator rights, and a saved administrator command-line session.
That is the hygiene failure. A decommissioned server still holding production keys is a known class of incident. Discord’s developer terms tell app owners to treat tokens as confidential, encrypt credentials, and use commercially reasonable safeguards. Discord’s own token UI hides a bot token after first view because a leaked token is the bot.
Once inside Google Cloud at 12:03, the attacker added an SSH key, opened a shell in a running bot container at 12:26, and read the Discord token. From there they were Double Counter, in every server that had invited the bot.
Their own support server was raided
A security bot is supposed to make this boring. On their support server the stolen token granted the attacker Administrator at 13:24, about fifteen roles at 13:26, and an unban after staff banned the account. Later, two webhooks posted attacker invites into that same server.
That is a raid of the vendor’s own Discord, using the vendor’s own bot. Discord’s Raid Protection 101, Pause Invites, Security Actions, and a tight role hierarchy exist so a single stolen token cannot walk the permission tree. /antinuke settings (Administrator) and /scan exist on BetterAntispam for the same reason: watch the audit log when a bot or a staff account starts granting Administrator.
This was avoidable with ordinary operations: shut down unused hosts, do not leave admin analytics on the public internet, do not leave cloud admin keys on those hosts, keep the bot token in a secret store (they moved it there after the theft), and monitor permission grants in real time (they turned that monitor on at 14:57, two hours after the token was read).
I am not going to pretend BetterAntispam is unhackable. No bot is. The lesson is smaller and meaner: if you store millions of member IPs and then leave a retired box attached to production, you are running a verification product on leftover infrastructure.
Verification died, and large servers sat in the dark

When you steal a Discord bot token, Discord sees a valid bot. Members see the usual green Verify button. The interaction then fails. The screenshot above is a public-facing verify channel: Double Counter posted “Click the green button below to verify,” the member clicked, and Discord returned The application didn’t respond in time. Chat is locked. Staff cannot even tell members what to do in that channel.
Double Counter’s timeline says the bot went offline when they invalidated the token at 13:39. Verifications resumed around 14:49, stopped again at 15:04 when the attacker changed the database password, resumed at 15:28, then the whole product was taken offline around 16:08 until 19:19. That is hours of dead gates on a bot that, according to third-party directory writeups, sits in on the order of 650,000 Discord servers.
I cannot honestly count how many people failed /verify that afternoon. I can say this: if a verify bot is the only door into hundreds of thousands of servers, an hours-long outage is mass confusion. New members sit unverified. Raiders who already got in stay in. Staff who trusted a third-party CAPTCHA have no fallback except native verification levels and Pause Invites.
From 13:30 the same stolen token posted the attacker’s Discord invite, as Double Counter, in about 50 large servers. The report names “Steal a brainrot” as the largest they confirmed. Those messages looked like the trusted verify bot talking. Substantially all were deleted later. If you still have a 4 October invite from Double Counter in the 12:00–16:30 UTC window, delete it and check your audit log, as they asked.
What was copied
This is why a verify-bot breach is worse than a leveling-bot breach. Double Counter’s own table:
| Data | Records | Status in the report |
|---|---|---|
| IP addresses linked to Discord ID and username (alts and verified users) | ≈ 27 million | Partly copied |
| User-agent hashes used for alt detection | ≈ 44 million | Copied |
| Emails (server admins, dashboard, Doogle, advertisers/API) | ≈ 1.3 million | Copied |
| VPN detection logs | ≈ 15 million | Not copied |
| Behavioural fingerprints | ≈ 25 million | Not copied (stored elsewhere) |
| Cold storage of user data and IPs | ≈ 58 million | Not affected |
They treat the full verified-user IP table as exposed because the copy was interrupted about 20% through and they cannot tell which rows left. Discord passwords were never in that database. Card numbers sit with the payment provider. Two Atis customer charges ($3 and $15) were refunded. Doogle users, advertisers, and API customers are told to expect phishing because their emails were copied.
A verification bot that keeps tens of millions of IP-to-Discord-ID rows is a high-value target. The breach made that concrete. It did not create the privacy argument. That argument was already public.
Doogle: verification data, paid search
Doogle is Double Counter’s paid alt-account search. Paste a Discord user ID. It lists other accounts the same person supposedly runs, graded certain, medium, or possible. Double Counter’s own docs say Doogle is powered by the same pipeline as verification, across more than 500,000 servers and 40 million unique user IDs. The person you search is never notified.
That is the product. A member clicks Verify to enter a Roblox or boosts server. The bot stores IP, user-agent, and association signals. A Doogle subscriber later pays $6.99 to $29.99 a month to search that graph. Double Counter’s privacy policy says they “do not sell or share your stored personal data” and “do not sell or share your IP address with third parties.” The same policy describes Doogle as a subscription that returns associated Discord accounts derived from “existing verification and detection processes.”
I will be precise. I have not seen a receipt that says “we sold your IP file.” I have seen a paid search product whose input is Double Counter verification and whose output is other people’s accounts, sold to whoever pays, without notifying the person searched. Moderators who want alt detection inside their server are not the whole customer. Anyone with a Doogle plan can look up an ID.
Their verification page also uses Ezoic for interest-based ads. That policy lists IP address, device type, OS, language, and browser as data that may be collected in cookies when ads are served. A verify click that funds advertising partners is a different kind of third-party share than Doogle, and it is in their legal text.
Reddit already called it a privacy invasion
The r/discordapp thread “isn’t this a privacy invasion?” is a year old, 2k upvotes, and still the search result people land on. The comments are mixed, which is honest.
On fingerprinting, one commenter in that thread wrote that Double Counter “requires you to verify yourself in a browser, which means that they have your browser fingerprint linked with your Discord account.” Another put it shorter: it “verifies users to find alts by aggressively fingerprinting them.”
On household false positives, a deleted account asked whether the tool would show Discord accounts of anyone you live with. A reply in the same thread answered “potentially.” That is the roommate and family problem: one home IP, many Discord IDs, a paid search that treats them as alts.
On legal pressure, u/altforweirdshit04 wrote: “Yes , there is currently a GDPR complaint and class action lawsuit in the works against the company that makes it.” That is a Reddit comment, not a docket number I can verify. Treat it as community belief, not a filed case. What is on the record is Double Counter’s own CNIL filing after this breach (FR2610050000001) and their Right to Erasure text, which still keeps “pseudonymized account-association linkages” for up to 24 months for fraud prevention.
r/privacy ran “This Popular Discord Bot Is a Privacy Nightmare.” Another r/discordapp post called Doogle a doxxing shortcut because a “chill” account and a work account on the same connection become one graph. A later thread is still asking whether to remove it.
I agree with the people who say server owners need some alt signal. I disagree that the answer is a global, paid, silent search of everyone who ever clicked Verify. /privacy opt-out that only works in a server where the bot is installed, and that you must repeat on every linked account, is a poor answer to “I never invited this company.”
YouTube and X did not miss it
No Text To Speech (about 1.74 million subscribers) covered the graph in Discord Alts Can Be Tracked Now.... The video walks Doogle opt-out, shows that opting out on one account is not enough, and argues family members on the same IP are outside your control. That is the same household-link problem Reddit raised. NTTS also flags Discord’s developer terms around advertising and user notice. I am quoting a public video, not claiming I audited their codebase.
On X, Panley (@panley01) wrote after this incident:
The Discord Bot, Double Counter, suffered a data breach & near complete takeover last week. They were not complying with GDPR, and got caught with data they shouldn't have. I wonder if Discord will take this illegal behaviour seriously, hard to feel bad for the developers here.
Panley is stating an opinion about GDPR. Double Counter’s lawyers will disagree. The factual half is not in dispute: they had a near takeover, they copied a database they should have been protecting, and they told CNIL.
What I would run instead
Native Discord first. Turn on AutoMod, a real verification level, and Raid Protection. That stack does not build a 40-million-ID search engine.
Then invite BetterAntispam if you want a bot. /setup (Administrator) picks a log channel. /verification settings (Administrator) is the gate: button (default), image CAPTCHA, math, or hidden word. Members run /verify. Staff can /force verify or /bypass. Website Captcha, from the same panel, sends the member to a one-time betterantispam.com link, Cloudflare Turnstile, and VPN / proxy / Tor / datacenter / alt checks. Our Website Captcha privacy page says staff see a summary (“VPN detected”, “linked to a banned account”), not the raw IP or fingerprints. In the bot, those correlations are stored as HMACs keyed with WEB_VERIFY_HMAC_KEY, not as a dump of IPs. Retention is measured in days and months, then pruned. We do not sell that graph. We do not offer a Doogle. We do not put an ad network on the verify page.
That is the privacy difference I will defend. Alt detection that stays inside your server, for your bans, is a moderation tool. Alt detection that anyone can buy and run against a user who never joined their server is a directory.
The rest of the protection stack is the same bot, still configured in Discord:
| Job | Command | Permission |
|---|---|---|
| Join raids | /antiraid settings, /raidmode enable | Administrator |
| Chat floods | /antispam settings | Administrator |
| Compromised staff / bot | /antinuke settings | Administrator |
| Trap channels | /honeypot settings | Manage Server |
| Dangerous overwrites | /scan | Administrator |
BetterAntispam has been on Discord since 2020. We have not had a public token theft or database export of this kind. I will not claim we are unbreachable. I will claim we do not productize member graphs for third parties, and we do not leave verification hanging on a single cloud token with a retired Metabase box behind it.
If anti-nuke against hostile staff is the whole job, Wick’s own intro is still the specialist read. If you only need reaction roles, keep Carl-bot. If you already paid for MEE6 Premium, keep it for XP. Do not keep a verify bot whose outage locks your entire onboarding and whose side product is a paid people-search.
For the minute-by-minute raid sequence, use the raid playbook. For gates without a global fingerprint broker, see member screening.
FAQ
Was Double Counter hacked?
Yes. Their 4 October 2026 report says an attacker used a vulnerability on a retired OVH server, reached Google Cloud, stole the Discord bot token, copied about 12 GB, and ran payment fraud on a sibling account. They say the incident is contained and the service was restored at 19:19 UTC.
Why did Double Counter verification stop working?
The bot went offline when the token was reset, then again when the attacker locked the database, then again when Double Counter took the product down to cut leftover access. During those windows, Verify buttons returned Discord’s “The application didn’t respond in time.” Anyone in a server that used Double Counter as the only gate could not finish onboarding.
Did they raid other servers?
The stolen token posted the attacker’s invite in about 50 large servers, appearing as Double Counter. The attacker also received Administrator on Double Counter’s own support server. That is both a customer-server incident and a vendor-server raid.
Does Double Counter sell user data?
Their privacy policy says they do not sell stored personal data or IP addresses. They do sell Doogle subscriptions that return alt-account associations built from Double Counter verification, and their verify page uses Ezoic advertising partners. Reddit, NTTS, and Panley treat that as monetizing verification data. I treat Doogle as a paid people-search on a verification graph, which is the privacy problem even if the policy avoids the word “sale.”
Is there a GDPR complaint or class action?
Double Counter says it notified CNIL on 5 October 2026 (FR2610050000001). A Reddit comment claimed a GDPR complaint and class action were “in the works” a year earlier. I have not independently verified a class-action filing. Members in the EU can still use /privacy and complain to a supervisory authority.
Is BetterAntispam a Double Counter alternative?
For verification, raids, nukes, and honeypots, yes. Run /verification settings (Administrator). We do not operate a public alt-search website. We have been running since 2020 without a public breach of this type. We still cannot promise every attack is stopped.
Which verification bot should you choose?
- Choose BetterAntispam when you want verification, VPN/proxy/alt checks, honeypots, anti-raid, and anti-nuke in Discord, without a paid directory of other people’s accounts.
- Choose Discord’s native tools when a verification level, AutoMod, and Pause Invites are enough and you do not want a third-party verify bot at all.
- Choose Wick when anti-nuke against hostile staff outweighs onboarding.
- Keep Dyno, Carl-bot, or MEE6 if they already own roles, tickets, or XP, and add a protection bot rather than a global fingerprint broker.
If you still run Double Counter, complete their /privacy flow on every account that ever verified, rotate any staff secrets you reused, and do not treat “contained” as “the copied rows are gone.” Copied data stays copied.
Double Counter’s October 2026 incident is a token theft, a verification outage, a vendor-server raid, and a database copy of a product that already sold lookups of the same graph. That combination is why I would not put a growing public server back on it.
Final Verdict
Read their incident report. Turn on Discord AutoMod and a verification level today. If you want a bot that verifies members, watches raids and nukes, and does not sell a people-search on top, invite BetterAntispam and run /setup, then /verification settings.
— Adam
More guides
- How to Stop a Discord Raid (2026 Playbook)
- Best Discord Moderation Bots in 2026
- Server Owners, Lock Role Hierarchy and Enforce 2FA
- Keyword Blacklist Discord: AutoMod Then a Bot
- Preserve 45 days of Discord audit logs
- Website Captcha privacy
- How to Protect Your Server from Raids 101 – Discord
- AutoMod FAQ – Discord
Sources
- Targeted attack on Double Counter’s infrastructure
- Doogle docs
- Doogle alt detection
- Double Counter privacy policy
- Discord Developer Terms of Service
- Why can’t I copy my bot’s token? – Discord
- How to Protect Your Server from Raids 101 – Discord
- Pause Invites FAQ – Discord
- Activity Alerts and Security Actions – Discord
- Verification Levels – Discord
- AutoMod FAQ – Discord
- Server Audit Log – Discord
- isn’t this a privacy invasion? – r/discordapp
- This Popular Discord Bot Is a Privacy Nightmare – r/privacy
- Double counter is invading users' privacy – r/discordapp
- Is double counter bad? – r/discordapp
- Discord Alts Can Be Tracked Now... – No Text To Speech
- Panley on X
- Is Double Counter Safe? – Peakbot
- Notify a data breach – CNIL
- Metabase installation docs
- BetterAntispam Website Captcha privacy